
DORA · EU banks
Audit rights on paper → artifact at handoff
When you need to practically exercise monitoring / audit rights under DORA Art. 30(3)(e)(i) on a code delivery — with a portable artifact for the acceptance file.
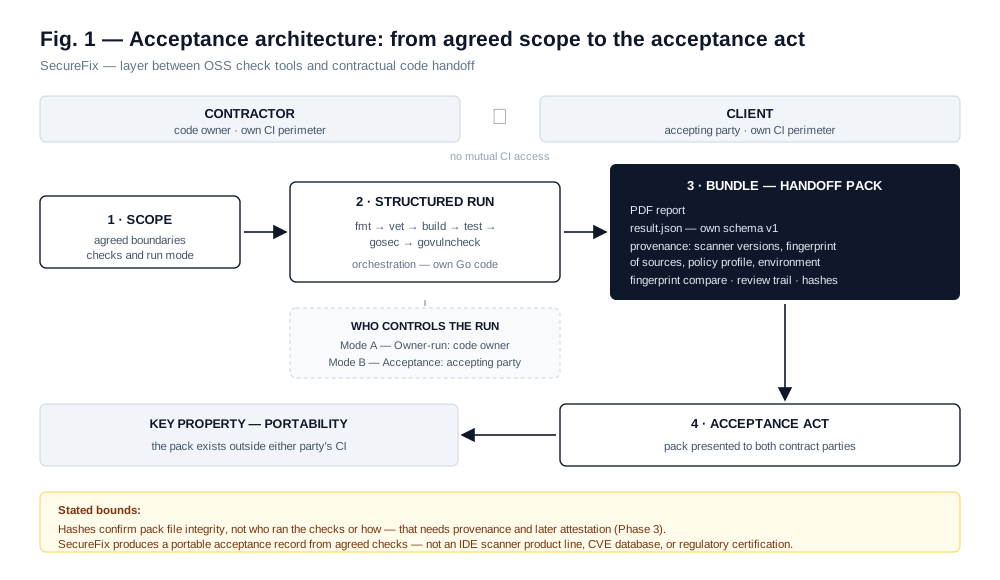
SecureFix produces one document both sides can check: what was run, with which tools, what was found, and what was sealed. It lives outside either party’s CI — so it survives the boundary between two companies.
You are not buying our good faith — you are buying the ability not to need it.
Owner-run by default: your code stays inside your own infrastructure. We never receive the repository.
Product 2.0 · Go · Python · JavaScript, including mixed delivery · integrity: SHA-256
$ securefix audit ./example-service
✔ fmt          passed
✔ vet          passed
✔ build        passed
✔ test         passed
⚠ gosec        findings recorded (demo)
✔ govulncheck  recorded

[•] Sealing Evidence Bundle…
↳ result.json + report.pdf · integrity hashes

✔ Bundle sealed — findings retainedDemo sketch (Go terminal). A real Bundle uses the same seal format for a single-language scope or a mixed delivery (Go + Python + JavaScript in one pack).
One product — three reasons to buy.
DORA · EU banks
When you need to practically exercise monitoring / audit rights under DORA Art. 30(3)(e)(i) on a code delivery — with a portable artifact for the acceptance file.
SOC 2 · ISO 27001
For B2B SaaS and teams that need portable proof of software-delivery controls at audit time — without claiming SecureFix “grants” SOC 2 / ISO.
DevSecOps
When Engineering / AppSec accept code from a vendor or another team and want a sealed trail: scope, tools, findings, review — outside the other party’s CI.
Head of Compliance
Close the gap “audit rights exist, but there is no portable record of the code handoff” — without buying another org certificate.
CISO
See what was actually checked at handoff, with pack integrity — instead of trusting the vendor’s green tick.
Engineering Lead
Agreed scope, recorded tool versions, and a review trail next to the sign-off — for the team and for the auditor.
Demo fixture · public sample scope · same Bundle schema for Python/JS

Color PDF preview. Full file opens in the browser.

B/W anatomy: human PDF · machine JSON · hashes / signature — one pack per delivery.
Trust Summary from the demo run — what an auditor / CISO sees.
Open PDFPassed demo run · 0 findings · fixture only.
Download ZIPFailed demo run · multiple findings · artifacts only.
Download ZIPAlso: all three Bundles, Python/JS rehearsal ×10, verify in browser, schema v1, legal. Product line: 2.0 · schema v1.
Three founders and an EU partner — product, engineering, finance, and business development. Operator-stage details: Legal.
CEO · product · pilots
Background as deputy director for finance and procurement: public contracts, supplier oversight, and formal acceptance of deliveries on the buyer side. Now runs SecureFix product, pilots, partner delivery, and go-to-market.
CTO, co-founder
8 years in software development, including 4 years on Go. Owns the audit pipeline, architecture, and core engineering.
CFO, co-founder
Background in tax administration and corporate/public-sector finance (including Gazprom and the Ministry of Finance). Runs SecureFix financial model, compliance, and operations finance.
Partner · EU business development
EU partner for design partners, pilots, and commercial outreach in Europe.
A bounded delivery — one repository, one commit, agreed check list. You also choose the run mode here: Owner-run (you run it, we never see the code) or Acceptance run (the receiving party runs it on what it was delivered). Nothing starts until the scope and the mode are agreed in writing.
Orchestrated stages with recorded tool versions by language (e.g. Go: gosec · govulncheck; Python: Bandit · pip-audit; JavaScript: eslint · npm-audit).
PDF + machine-readable evidence with integrity checks — outside either party’s CI.
Two modes. You choose before any code moves.
You run SecureFix yourself, inside your own perimeter. We never receive the repository. You send us only the sealed Bundle — or nothing at all, if you just want the artifact for your own acceptance file. Nothing about your source code leaves your infrastructure.
The receiving party runs the checks on a delivery it has already been given under the contract. The code stays between the two contracting parties. SecureFix does not sit in the middle.
In both modes: the sealed pack lives outside either party’s CI. That is the point of the product — the artifact has to survive the boundary between two legal entities.
If a scope genuinely requires us to run the checks on your code, that is a separate written arrangement with an NDA, a named retention period, and deletion on completion. It is never the default and never happens silently.
In Owner-run, no. You run the tool; we receive nothing. Access is only ever granted by explicit written agreement for a specific scope.
Findings, tool names and versions, a fingerprint of the sources, the policy profile, environment data, and integrity hashes. It does not contain your source code.
With you. We keep a copy only if you ask us to, for a period you set.
Yes, before any scope discussion that involves non-public information.
No. It is a visual layout preview that runs in your browser.
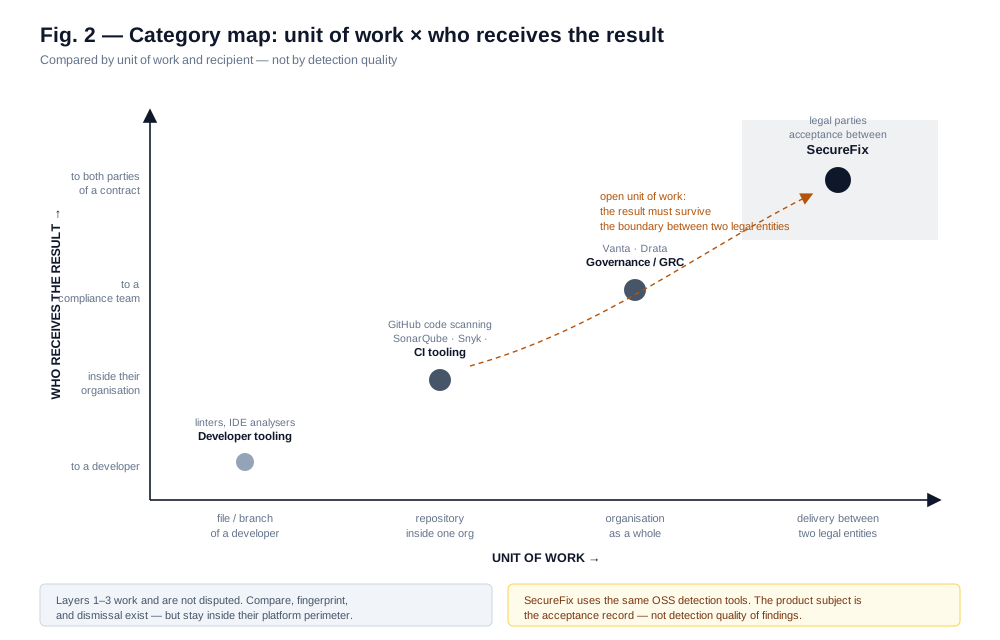
CI scanners (gosec, Bandit, eslint, npm-audit, etc.) produce findings inside your pipeline. SecureFix adds a portable acceptance pack for both sides at handoff: PDF + hash-checked Evidence Bundle, recorded tool versions, and a recorded human review step — without requiring the other party to trust your CI logs alone.
| CI scanner | SecureFix | |
|---|---|---|
| Main output | Findings in the pipeline | Portable acceptance pack (PDF + Bundle) |
| Where it lives | Usually inside one CI | Can run outside either party’s CI |
| Integrity of the pack | Usually not packaged as a sealed handoff artifact | Hash-checked Evidence Bundle |
| Operator review | Optional / outside the tool | Designed into the acceptance record |
| Category | Findings in a pipeline | Acceptance / audit-record pack for handoff |
Now = Product 2.0 acceptance pack (Go / Python / JavaScript). What comes next: product roadmap.

Paste a short Go snippet — visual preliminary layout only (nothing uploaded). A full Evidence Bundle is produced in the run environment you choose — see Where your code runs.
SecureFix is software you run, not a consulting engagement. Two ways to get it:
No retainer. No hourly billing. No dependency on our calendar.
Write to info@securefix.pro and include: company, language (Go / Python / JavaScript), scope size, and timeline.
We reply with clarifying questions if needed, then a priced offer for that scope.
Offer without obligation to order our services. Pricing after scope review.
By contacting us you agree to the legal notice.